Is an Online TOTP Generator Safe? Technical Security & Privacy Analysis
The Security Tradeoffs of Web-Based 2FA Generators
Two-factor authentication is intended to be “something you have.” When using an online web tool to generate authentication codes, cybersecurity professionals naturally ask: Is it safe to paste a 2FA secret key into a browser?
The answer depends entirely on the technical architecture of the web tool in question. Understanding the difference between server-side generation and client-side Web Crypto execution is critical for assessing risk.
1. The Dangerous Model: Server-Side Generation
Poorly architected or malicious online utilities send your secret key to their backend server via an HTTP POST request, calculate the TOTP code on the server, and return the digits in a JSON response. This model is inherently unsafe:
- The secret key traverses the internet and can be logged in web server access logs.
- The server operator could store secrets in a database for unauthorized access.
- Any vulnerability or compromise of the remote server exposes your accounts.
2. The Secure Model: 100% In-Browser Web Crypto Execution
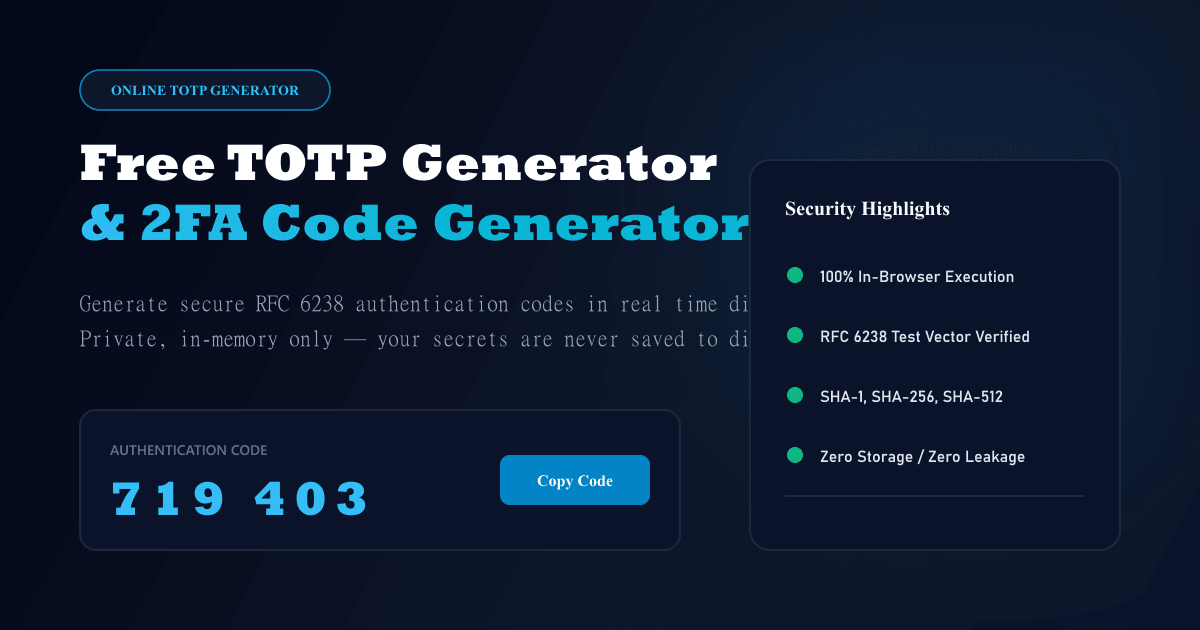
Legitimate, privacy-engineered tools—including our TheFBace TOTP Generator—use the native browser Web Crypto API (window.crypto.subtle):
- Zero Network Requests: Open your browser Developer Tools (F12) and inspect the Network tab while generating a code. You will observe that zero HTTP requests are transmitted when you paste a key or generate digits.
- Zero Persistent Storage: A properly audited tool avoids
localStorage,sessionStorage, and cookies. All cryptographic HMAC operations run in volatile JavaScript RAM and are permanently purged on tab closure. - Open Standard Compliance: The algorithm strictly implements public RFC 6238 mathematical specifications.
3. Real Threat Vectors to Consider
Even with pure client-side processing, web-based generation has operational risk factors compared to dedicated physical hardware:
- Malicious Browser Extensions: Browser extensions with broad permissions (“Read and change all your data on the websites you visit”) can intercept input field contents. Ensure you run privacy-sensitive tools in an Incognito window with extensions disabled.
- Session Replay & Analytics Scripts: Commercial tracking tools (such as Hotjar or FullStory) can inadvertently capture user inputs if not explicitly configured with masking rules. TheFBace strictly excludes the entire 2FA tool container from telemetry and session recording.
- Clipboard Hijackers: Desktop malware can monitor your operating system clipboard to replace copied authentication codes or secrets.
4. When Should You Use an Installed Authenticator App?
Online generators provide exceptional utility when managing authorized shared business assets, running emergency desktop logins, or working on systems without mobile phone access. However, for your primary personal email and banking master credentials, an installed hardware security key (FIDO2 / WebAuthn YubiKey) or an encrypted mobile authenticator (Google Authenticator, Apple Passwords) remains the gold standard.
Learn how to safely move credentials to a mobile device with our guide on how to transfer authenticators to a new phone.